
Manage the sprawl
Observability and management: Ten agents, one set of rules on Rails. Adding the eleventh doesn't mean adding an eleventh version of them. Rails is built for enterprise complexity.
Agent policy-as-code to control what every agent can browse, spend, and deploy at run-time - before they act
Not a customer yet? Join the Waitlist
30 day free trial. No credit card required. After trial, choose
custom, annual, or monthly plan based on usage.
TRANSCEND Agent CONTROLS
Transcend Rails is the agent policy-as-code platform that controls agents and everything they touch. Every action an agent proposes is checked at runtime and resolves to allow, deny or escalate before it happens.
Observability and management: Ten agents, one set of rules on Rails. Adding the eleventh doesn't mean adding an eleventh version of them. Rails is built for enterprise complexity.

Permissions and sensitive data: A scheduling agent reads a medical appointment summary to book a follow-up. Only permissioned clinical data reaches the model. Rails never touches PII or your keys.

Enable operations and revenue: A media company's CMS offered agents full write access or nothing. With one Rails policy, read but never write, editors now work with agents on live content.
Agents are resourceful. If one path to a system or a dataset is closed, an agent will find another: a direct model call, an API request, something it remembers from an earlier task. A single gateway sees only the traffic that passes through it, so Rails checks policy at all five points an agent acts through.
Control point
Transcend
Inference
Model calls: data use, model access, PII and prompt-injection checks on what goes in and what comes back
MCP (Tools)
MCP tool calls and connectors: the specific operation on the specific resource
Network
Web and API requests
Memory
What the agent may retain and write back
Secrets
API keys and credentials that your agent can use
TRANSCEND Agent CONTROLS
Identity tools decide who an agent is. Gateways decide what it can reach. GRC tools document what it should do. Transcend Rails decides what the agent actually does, action by action, and can stop it before it happens.
Every agent, internal or third-party, calls one runtime decision point before it acts. We integrate with your identity providers (e.g. Okta, WorkOS) to import existing roles. Allow, deny, or escalate comes back.
Covers Claude Desktop, Claude Code, Cursor, AWS Bedrock and AgentCore, Snowflake Cortex, Adobe Experience Platform, Databricks, and more. It speaks MCP with open-source SDKs, so there's no proprietary client and no data plane rewrite.
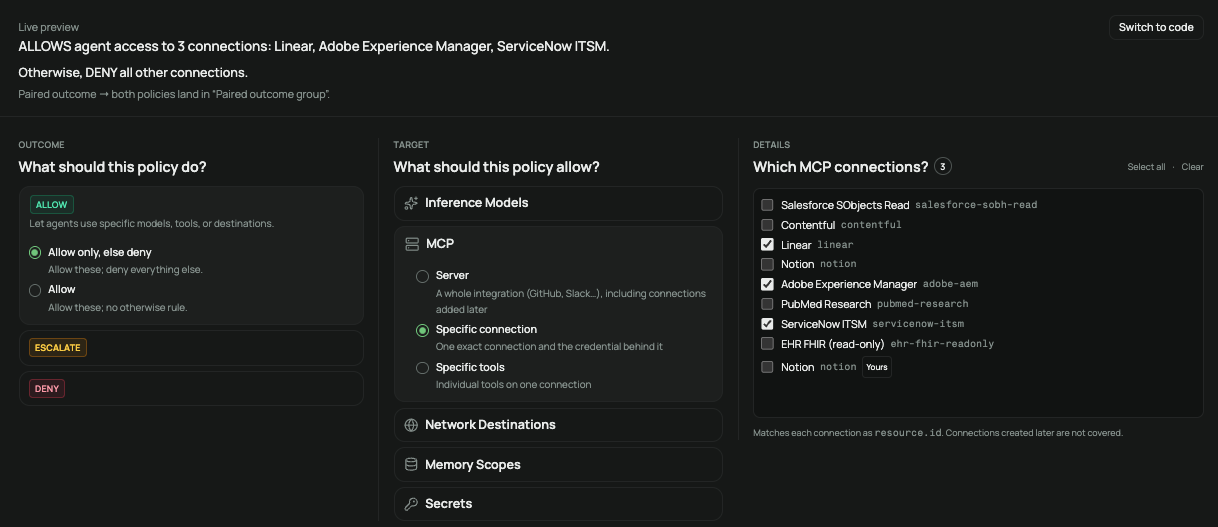
Policies are written in plain language and translated into Rego with standardized versioning. Each new policy and update is simulated against real agent traffic before it rolls out. The enterprise baseline is inherited by every brand and use case.
Inference, tool calls, network, memory and the secrets are all governed by the same policy set. Default fail-close (business can also write custom override). Low latency, P95 <75ms SLAs
Decisions run inside your cloud, Transcend's zero-trust gateway. Keys stay with you, including through your own KMS with HSM-backed management. Transcend never sees your data. Designed for the most sensitive data use cases.
Every decision is logged, with nothing sampled. Each record shows the agent, its owner, the rule, the policy version and the approver. A kill switch stops any agent on any stack, and an agent is quarantined when its owner leaves. Immutable, OTEL compatible audit trail.